
Product Introduction⚓︎
[Important Notice | JumpServer Vulnerability Notification and Remediation (JS-2026.09.09)]
In August 2026, the JumpServer open source project team received vulnerability reports from security researchers. After verification, the following vulnerability was confirmed:
■ JumpServer SQL query filtering leads to access key leakage vulnerability. Details: GHSA-6rp5-ff2m-qfrm
Exploitation conditions:
Any logged-in regular user can obtain the administrator's Access Key without authorization by appending specific parameters to an API request.
Affected versions:
JumpServer V3: >= 3.7.0 and < v3.10.23 LTS
JumpServer V4: >= 4.0.0 and < v4.10.19 LTS
Secure versions:
JumpServer V3: >= v3.10.23 LTS
JumpServer V4: >= v4.10.19 LTS
Remediation:
Upgrade the JumpServer bastion host (including Community Edition and Enterprise Edition) to a secure version.
Temporary remediation:
Disable the following related filtering parameters in the nginx configuration file:
-
If HTTPS is enabled, this can be done by modifying the /opt/jumpserver/config/nginx/lb_http_server.conf configuration file;
-
If HTTPS is not enabled, you need to modify the /etc/nginx/conf.d/http_server.conf configuration file in the jms_web container, and then execute the container commit to save the changes. After the update is complete, restart the jms_web container.
location / {
    if ($args ~* "(^|&)(_|%5f)(r|%72)(e|%65)(l|%6c)=") {
        return 400;
    }
    .....
}
curl -sk -o /dev/null -w '%{http_code}\n' 'http://<address>/api/v1/users/users/?_rel=not'    # Expected 400
curl -sk -o /dev/null -w '%{http_code}\n' 'http://<address>/api/v1/users/users/?%5Frel=not'  # Expected 400
curl -sk -o /dev/null -w '%{http_code}\n' 'http://<address>/api/v1/users/users/'             # Expected 401/403
1 What is JumpServer?⚓︎
JumpServer is a popular open source bastion machine that is a professional operation and maintenance security audit system conforming to the 4A specification. JumpServer helps enterprises manage and log in to all types of assets in a more secure way, implementing pre-authorization, in-process monitoring, and post-audit to meet compliance requirements.
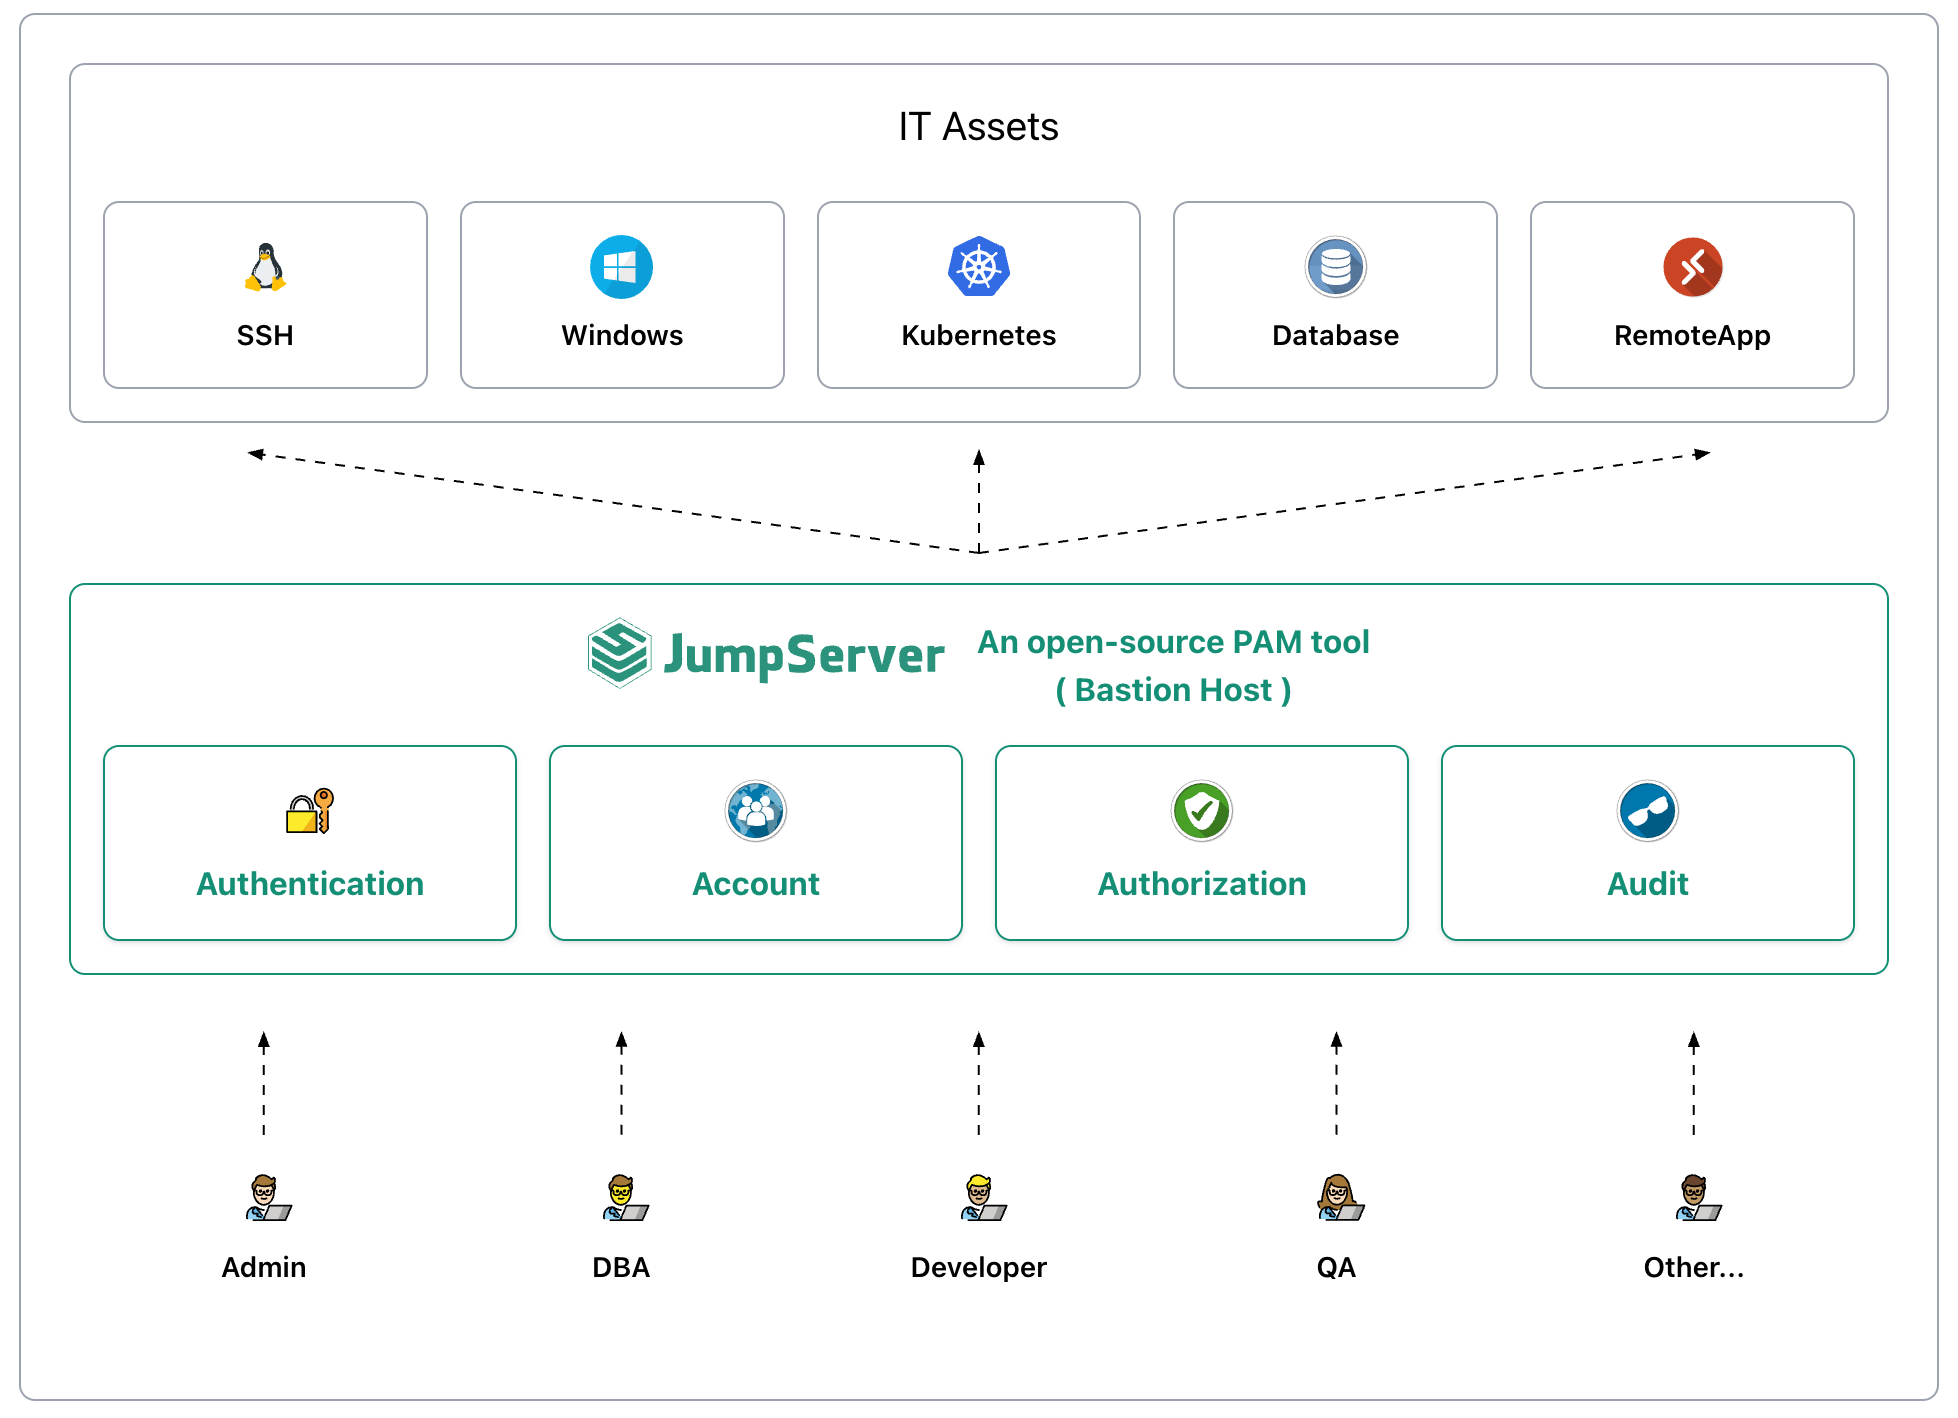
JumpServer bastion machine supports the following asset types:
- SSH (Linux / Unix / Network devices, etc.)
- Windows (Web access / native RDP access)
- Database (MySQL / MariaDB / Oracle / SQL Server / PostgreSQL / ClickHouse, etc.)
- NoSQL (Redis / MongoDB, etc.)
- GPT (ChatGPT, etc.)
- Cloud services (Kubernetes / VMware vSphere, etc.)
- Web sites (Web management backends of various systems)
- Applications (various applications accessed through Remote App)
Documentation Guide
Official Website Installation and Deployment Online Demo Enterprise Edition Trial Community Forum Video Teaching Technical Whitepaper
2 Product Features⚓︎
JumpServer product features include:
- Open source: Zero threshold, quickly obtain and install online
- Distributed: Easily support large-scale concurrent access
- Plugin-free: Browser only, ultimate Web Terminal experience
- Multi-cloud support: One system managing assets across different clouds
- Cloud storage: Audit recordings stored in cloud, never lost
- Multi-tenant: One system for multiple subsidiaries and departments
- Multi-application support: Database, Windows remote applications, Kubernetes
3 Page Display⚓︎

4 Application Store⚓︎
JumpServer's remote application feature supports Chrome and DBeaver applications by default in community edition, and supports richer remote applications in enterprise edition. Click Application Store to get more remote applications.
5 Security Statement⚓︎
- JumpServer is a security product. Please follow basic security recommendations for installation and deployment.
- If you discover security issues, please contact us directly: support@fit2cloud.com